Overnight from November 1 to 2, 2026, a cyberattack disrupted refrigeration systems at dozens of stores in Belgium and several other European countries. Refrigeration units were switched into defrost mode, raising temperatures and leading to food losses. For readers who use or manage connected devices, the incident shows how specialized equipment linked to an IT system can become an entry point to an essential operation, in this case, food preservation.
Refrigeration equipment controlled remotely or tampered with
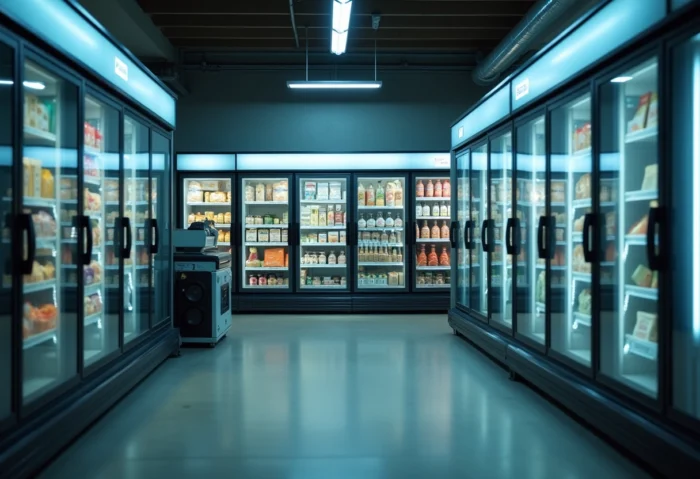
The mechanism reported by Euronews did not involve targeting checkout counters or payment terminals. The attack targeted control of refrigeration equipment. According to Stephan Moelans, head of Sabcobel, the units’ evaporators were put into defrost mode. This cycle, designed for normal equipment operation, causes temperatures to rise when activated on the affected equipment at the wrong time or repeatedly.
Defrost mode is a technical function, not a malfunction in itself. Refrigeration equipment must manage frost that forms on certain parts of the system. But when a computer command can change how the equipment operates, the security of the control system becomes as important as the security of the equipment itself. In this case, the physical consequences are immediate: stores must check temperatures and remove products that can no longer be safely stored.
The available information does not specify how the attackers gained access to the systems or whether the same method was used in each country. The attackers’ identities remain unknown. Euronews reports, however, that supplier Danfoss blamed the use of outdated software and said some customers had not installed recommended updates. Sabcobel, for its part, says a software update alone is not enough in every case and that hardware changes may be necessary.
Stores affected in several countries
In Belgium, the affected chains include Delhaize, Carrefour and Intermarché. IKEA also reported an incident at its store in Mons. According to figures reported by Euronews, about 40 Delhaize Proxy stores, 15 Carrefour Shop & Go locations, 15 Intermarché stores and five Spar Q8 gas stations were affected. Carrefour said 15 of its 700 stores were affected and that none were hypermarkets. The affected stores remained open, according to the chain.
Incidents were also reported in Sweden, the Netherlands, Estonia, Luxembourg, Finland and Ireland. Reports included ICA stores in Sweden, 13 SuperValu stores in Ireland and a Selver supermarket in Estonia. In Luxembourg, Delhaize suspended its ordering systems as a precaution. The available data do not provide a consolidated estimate of losses across all the countries. In Belgium, media outlets reported temperatures reaching as high as 70°C in some refrigerators and the destruction of food worth several hundred thousand euros.
The Belgian federal prosecutor’s office has opened an investigation. It is intended to establish the circumstances of the incident, but published information does not yet identify a group or individual responsible for the attack. Euronews says similar systems were targeted in France in October. The comparison concerns the type of equipment and the reported mechanism, but does not establish that the attacks were carried out by the same perpetrators.
What the incident shows about connected devices
A connected device is not necessarily a desktop computer or a phone. In a retail business, control systems can oversee refrigeration, lighting or other technical equipment. Once they are connected to a network and controlled by software, their configuration, access and maintenance are also cybersecurity concerns. A weakness in a specialized system can therefore have physical and operational effects, even when customer data are not at the center of the incident.
For organizations that operate this type of equipment, the measures mentioned in the sources are practical: keep software up to date, review vulnerabilities flagged by suppliers and assess whether a hardware change is necessary. Sabcobel also cites controlling refrigerators through a secure internet connection. These steps require coordination among IT teams, facilities managers and suppliers, because updating industrial equipment is not always handled in the same way as updating a standard computer.
For the general public, the incident is mainly a reminder that cybersecurity also affects the physical services retailers depend on. Customers cannot check the configuration of a store’s refrigeration systems themselves, and the sources do not mention any specific instructions for them. The key point is that network security does more than protect files: it also helps keep equipment running that preserves products and allows a store to continue operating.